
As CMMC enforcement ramps up across the Defense Industrial Base (DIB), contractors are racing to align their cybersecurity practices with new requirements. One often overlooked, yet critical factor driving compliance is the Federal Acquisition Regulation, specifically 48 CFR. This section of the Code of Federal Regulations governs procurement across federal agencies, and its impact on the Cybersecurity Maturity Model Certification (CMMC 2.0) is both direct and far-reaching. For organizations bidding on or maintaining Department of Defense (DoD) contracts, understanding the interplay between 48 CFR and CMMC 2.0 isn’t optional, it’s essential. (more…)
Category: Compliance Standards
Staying informed about all of the cyber security compliance standards is essential to keeping your company safe from hackers. Read on to learn about the various steps you can take to stay up to date with your industry’s compliance standards.
-
Guide to HIPAA Compliance Self Assessment
Companies directly or indirectly involved in healthcare must navigate HIPAA compliance requirements. A key part of maintaining compliance is performing regular HIPAA self-assessments. Whether conducted independently or with the guidance of experienced professionals, these audits help prevent costly violations while strengthening overall cybersecurity and data protection strategies.
(more…)
-

Who are the CMMC-AB and What do They Do?
CMMC-AB plays a central role in how organizations achieve compliance with the Cybersecurity Maturity Model Certification (CMMC), the Department of Defense’s framework for protecting Controlled Unclassified Information (CUI).
CMMC will be required for organizations that contract with the U.S. Department of Defense (DoD). While these contracts can be highly valuable, they require meeting strict cybersecurity standards. To achieve certification, organizations must be assessed by a qualified third-party assessor that is accredited by the CMMC Accreditation Body (CMMC-AB).
In this article, we explain who the CMMC-AB is, what it does, and how it fits into the broader CMMC ecosystem, including the other key stakeholders responsible for enforcing and maintaining CMMC requirements. (more…)
-
What is the HIPAA Enforcement Rule?
For businesses in the healthcare industry, the Health Insurance Portability and Accountability Act of 1996 (HIPAA) is essential for keeping clients and stakeholders safe. HIPAA defines what counts as “protected health information” (PHI), and its three prescriptive rules (Privacy, Security, and Breach Reporting) ensure its protection. The fourth, the HIPAA Enforcement Rule, defines what happens when a company fails to follow the other three.
-
Regulatory Comparison: CMMC vs. FedRAMP
If your company wants to win contracts with the US Department of Defense (DoD) or other government agencies, staying on top of cybersecurity requirements is essential. Two key frameworks you need to understand are CMMC and FedRAMP, both set standards for protecting sensitive information, but they apply in different ways. In this article, we break down CMMC vs. FedRAMP to help you navigate regulatory compliance and secure government contracts with confidence. (more…)
-

Ensuring HIPAA Compliance in Telemedicine: A Comprehensive Guide
For healthcare providers, securing electronic protected health information (ePHI) has become more complex with the widespread adoption of telemedicine .As ePHI is now transmitted in real time over digital platforms, the landscape of data protection and regulatory compliance has changed significantly. While telemedicine offers faster patient communication and improved access to care, it also introduces new risks, particularly around data security.
A single breach can result in serious consequences, especially if providers fail to follow HIPAA guidelines on telemedicine.
Fortunately, many of these risks can be reduced by adhering to the official HIPAA framework for telehealth. But what exactly do the HIPAA guidelines on telemedicine require? Let’s explore the key considerations. (more…)
-
Conducting a CMMC Readiness Assessment Step-by-Step
Companies that want to work with the Department of Defense (DoD) must meet high cybersecurity standards to safeguard sensitive government data. As part of the Defense Industrial Base (DIB), these companies are subject to rigorous compliance frameworks—including the Cybersecurity Maturity Model Certification (CMMC) —and must prioritize CMMC readiness early in the process. A readiness assessment is often the first step in preparing for official CMMC certification. It evaluates existing controls, identifies gaps, and guides organizations toward full compliance.
This blog outlines how to conduct a CMMC readiness assessment in three critical steps:
- Gauge existing controls against CMMC standards
- Execute a mock CMMC audit based on Practices and Levels
- Augment your security architecture to close any gaps
-
Who Can Decontrol CUI?
rsi security Organizations working closely with government entities, such as the U.S. military, often handle sensitive information, including Controlled Unclassified Information (CUI). For national security, it’s critical to manage CUI properly, including knowing who can decontrol CUI and how to safeguard it.
Understanding the processes for controlling and decontrolling CUI ensures your organization meets compliance requirements and protects sensitive data. In this guide, we break down the responsibilities and steps your team may need to follow
(more…)
-
What is Controlled Unclassified Information?
Companies working with the Department of Defense (DoD) regularly handle sensitive data. To maintain preferred contractor status, they must comply with cybersecurity frameworks such as the Cybersecurity Maturity Model Certification (CMMC). A key focus of CMMC is protecting Controlled Unclassified Information (CUI), a category of sensitive, unclassified data that requires careful handling.
Understanding Controlled Unclassified Information and implementing proper security measures is critical for compliance and safeguarding national security. (more…)
-
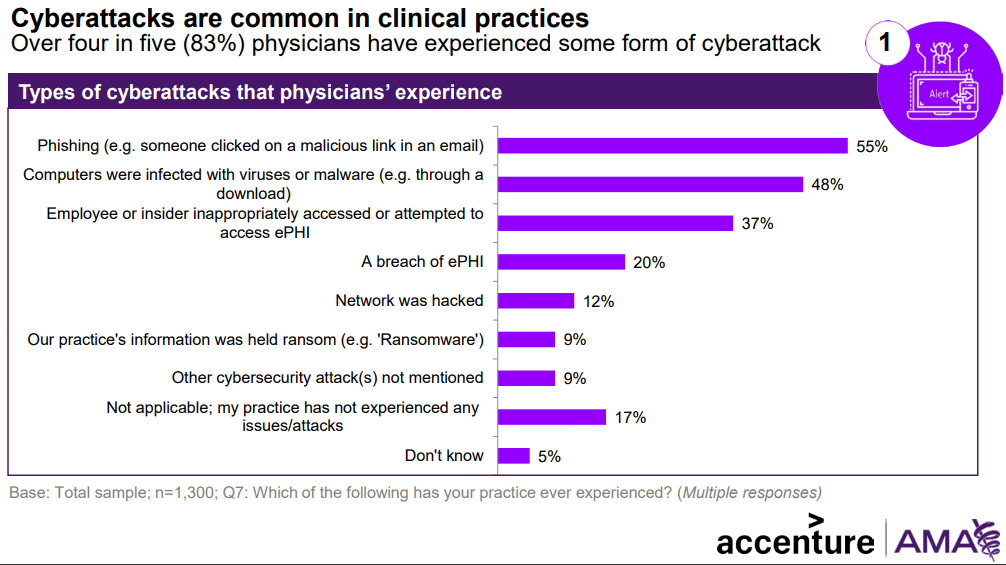
Medical Cyberattacks
A groundbreaking survey by the American Medical Association (AMA) found that 83% of U.S. physicians have experienced cyberattacks, highlighting the urgent need for improved healthcare cybersecurity. Among the 1,300 physicians surveyed in the December 2017 AMA report, many expressed dissatisfaction with federal support in protecting their practices and patient data. The survey revealed that three-quarters of physicians were most concerned about business disruptions and compromised electronic health records, while nearly two-thirds reported losing up to four hours of productivity following a breach. Alarmingly, 12% lost one to two full days of work. (more…)