
Patients’ medical records are some of the most attractive targets for theft. The US Department of Health and Human Services (HHS) designated them as protected health information (PHI) in the Health Insurance Portability and Accountability Act of 1996 (HIPAA) and laid out measures to ensure their safety. Later, the HITECH Act of 2009 updated these safeguards for the modern era. But what are the major components of the HITECH Act? (more…)
Category: Compliance Standards
Staying informed about all of the cyber security compliance standards is essential to keeping your company safe from hackers. Read on to learn about the various steps you can take to stay up to date with your industry’s compliance standards.
-
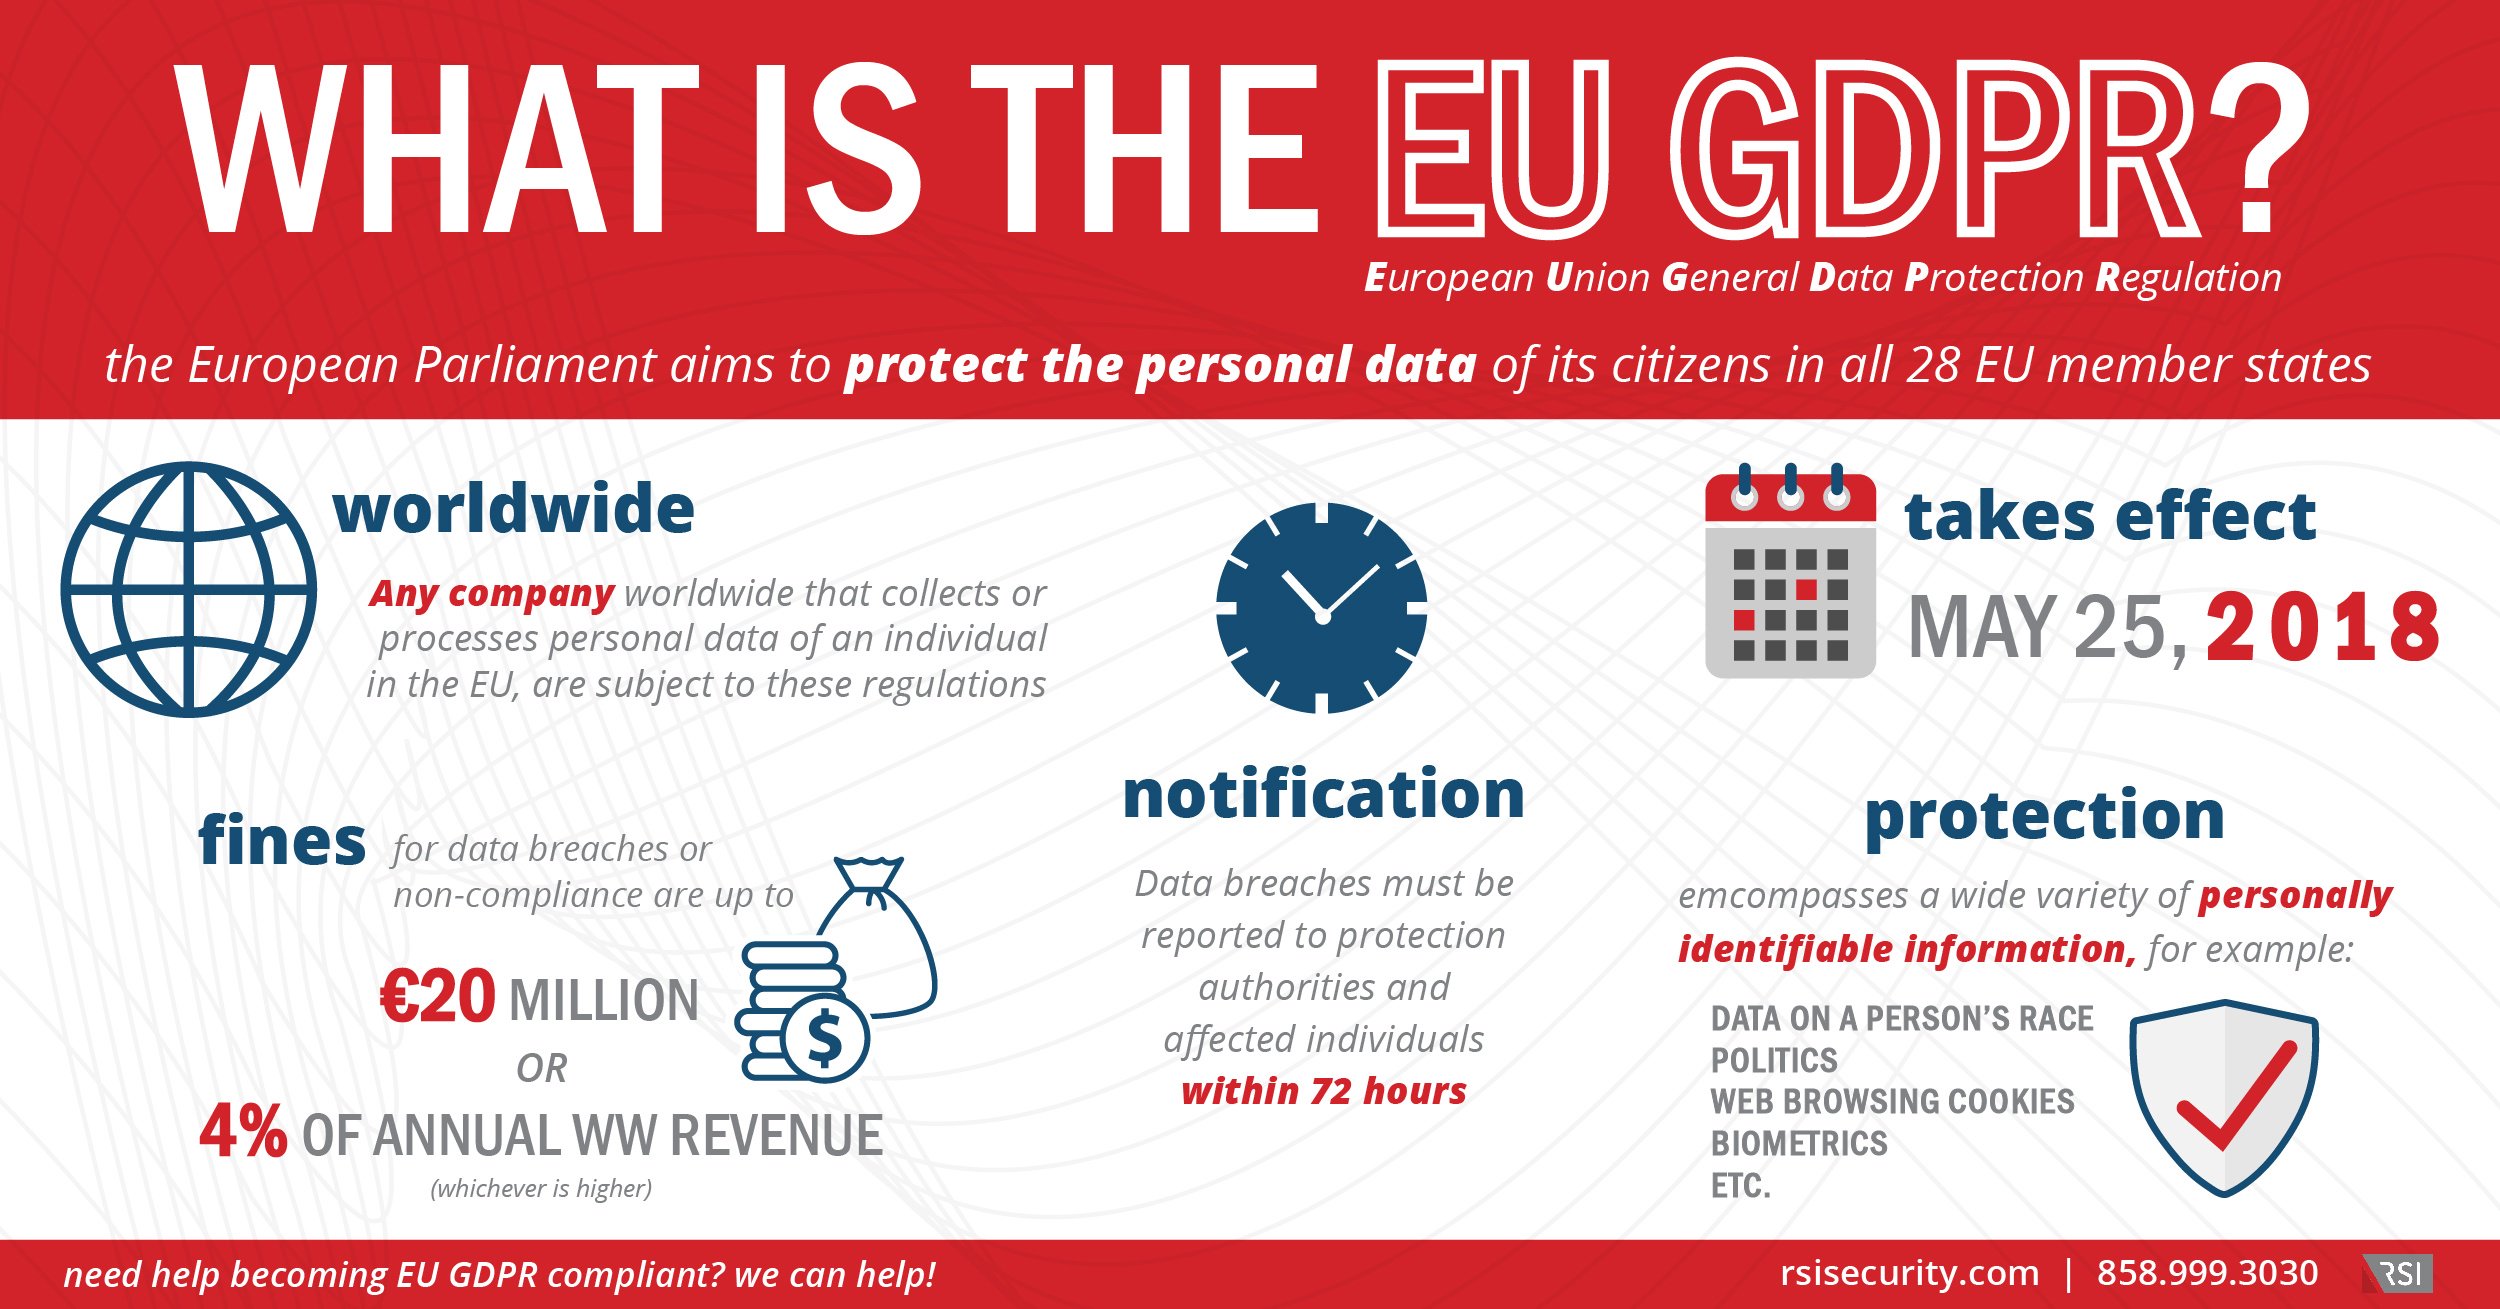
EU GDPR Explained
The impending European Union General Data Protection Regulation (GDPR) represents a sea-change in a company’s security strategies, transcending checkbox compliance programs.
-
How to Achieve Cryptocurrency Security Standard (CCSS) Compliance
Without a doubt, Bitcoin, cryptocurrency, and the blockchain are in the process of revolutionizing the entire landscape of global finance. Experts from major think tanks like the MIT Technology Review are predicting that cryptocurrency growth isn’t expected to slow anytime soon. As the cryptocurrency industry becomes more prevalent in various aspects of our personal and business lives, so is the need for regulatory standards to ensure transactions take place in a safe, secure manner. Which is exactly why the Cryptocurrency Security Standard (CCSS) was developed.
-
How ASVs Streamline PCI Compliance Scans
If your organization is working toward PCI certification, a PCI vulnerability scan is an essential step. These scans must be performed by a PCI Approved Scanning Vendor (ASV) to meet specific PCI DSS requirements. While ASVs are officially required for external vulnerability testing, trusted providers can also help strengthen your overall compliance program by offering tools and guidance across every stage of implementation.
(more…) -

How to Implement the CIS Controls Framework Efficiently
Organizations looking to install the CIS Controls need to understand the scope of the overall framework, along with the specific practices they need for their target Implementation Group. Then, once all controls are in place, they’ll need to conduct an assessment for verification. (more…)
-
Do You Need to Implement the CIS Critical Security Controls?
Understanding whether you need to implement the CIS security controls comes down to: (more…)
-
PCI DSS 4.0 – Understanding the working of PCI DSS 4.0
In 2019, the Payment Card Industry Security Standards Council (PCI SSC) began taking feedback for improving version 3 (v3.2) of the Payment Card Industry Data Security Standards (PCI DSS). With the new feedback, PCI SSC hopes to publish the final version 4 (v4.0) by 2021. Wondering how PCI DSS 4.0 will work? Get all your questions answered with our comprehensive guide. (more…)
-
SOC 2 Type 1 vs. Type 2: What’s the Difference?
SOC 2 Type 1 vs Type 2: Your SOC 2 Guide to Compliance
In 2025, cybersecurity threats are more sophisticated, frequent, and costly than ever. A recent IBM report found the average cost of a data breach has surged to $4.88 million dollars globally. For service providers, especially SaaS and cloud vendors, SOC 2 compliance has become a business imperative. Buyers want proof that their vendors can protect sensitive data, and understanding the difference between SOC 2 Type 1 vs Type 2 reports is key to earning that trust. SOC 2 delivers that proof. -
Understanding the PCI DSS 4.0 Roles and Responsibilities
In PCI DSS 4.0, roles and responsibilities play a central role in ensuring compliance, especially under the new Customized Approach. Organizations using this flexible method must clearly define and implement their responsibilities before assessors can issue formal compliance reports.
(more…) -
Which is Better: PCI DSS 4.0 Compensating Controls or Customized Approach?
Understanding the difference between PCI DSS 4.0 compensating controls vs customized approach is essential for achieving and validating compliance effectively. Compensating controls apply when specific PCI DSS 4.0 requirements can’t be fully met, while the customized approach allows organizations to meet security objectives through alternative methods. Both strategies help businesses maintain flexibility and strengthen their PCI DSS 4.0 compliance posture.
(more…)