
It’s not only merchants that are affected by PCI DSS 4.0, but payment facilitators will also need to make changes to their cybersecurity protocols. Payments Facilitators (PayFacs) must follow the same procedures as companies to ensure that personally identifiable information (PII) is secure from breaches.
Category: PCI DSS
Stay up-to-date with PCI DSS compliance. Explore in-depth guides, implementation steps, and best practices to safeguard payment data and meet regulatory standards.
-
What Does it Mean to Be PCI DSS 4.0 Compliant?
Any company that uses and handles credit or debit payment information from consumers needs to comply with PCI DSS, short for Payment Card Industry Data Security Standard. These standards cover technical and operational practices for handling cardholder data. Maintaining payment security is becoming more and more crucial as cybercrime becomes increasingly prevalent in our world.
-
What to Expect With PCI DSS 4.0: A Complete Guide
Any business or organization that accepts and/or processes credit and debit cardholder information should already be familiar with PCI DSS v. 3.2.1. Merchants are expected – and required – to meet this standard. This has been the case since 2018.
-

What Does Common Point of Purchase Mean For Your Business?
Criminals prey on ATMs, gas station pumps, merchant Point-of-Sale (POS) terminals and any other device that will provide them with the debit card information. Once they have the right information, they duplicate the cards and use them multiple times at the common point of purchase (CPP) to drain customers’ accounts.
-
How to Have Early Detection of a Common Point of Purchase
Do you own a business? If you do, it is probably associated with a CPP (Common Point of Purchase). This doesn’t mean that fraudulent purchases were made at your business, only that it was the target of a security breach. This could mean that your customers’ credit card information was compromised.
-
How to Prevent a Data Breach At a Cannabis Dispensary
Recent numbers indicate that the global legal marijuana market is expected to reach $146.4 billion by the end of 2025. A survey by Grand View Research further added that medical marijuana will likely dominate the market a few years from now with a projected value of $66.3 billion.
-

PCI Expert Summit 2019: Event Recap
RSI Security’s first-ever PCI Expert Summit is in the books, and we couldn’t be happier about how things turned out!
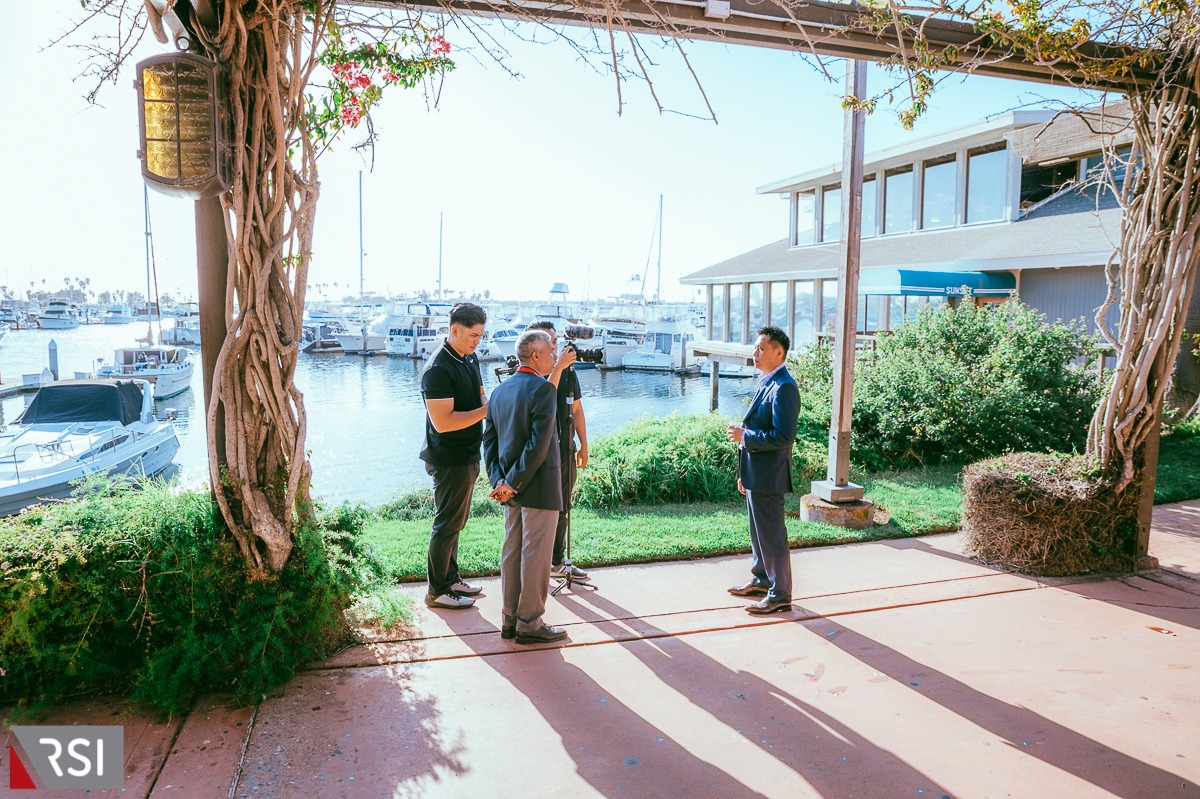
Marina Village Conference Center – San Diego, California On October 2nd we were joined by four speakers, a number of sponsors, an expert panel, and over 70 attendees to begin the process of building a strong, vibrant PCI compliance community in the Southern California area. The event took place at the beautiful Marina Village Conference Center in San Diego.
“I found the event to be very informative. It was also nice to be around other folks I’ve worked with previously but haven’t actually met in person. It was definitely worth the time coming down for what I hope to be the first of many future RSI Summits,” said Gurpal Singh, head of compliance at Finix Payments.
-
How To Avoid PCI Noncompliance Fees
Just as professional athletes or motorists pay fines when they break certain rules, the same applies to companies doing business online. But the rules governing these companies’ behavior goes beyond “unsportsmanlike conduct” or “following the speed limit.” When they collect and process payment information for debit and credit cards, they must adhere to a number of rules in the process. If they break those rules, then they’re on the line to pay a penalty for it.
If it’s expensive to ignore the rules, why are an increased number of companies doing so? Verizon’s 2018 Payment Security Report reveals a drop in PCI compliance, which are the standards that companies have to stick to in order to process payment information online. Where 55.4 percent of companies were compliant in 2017, that number shrank to 52.5 percent in 2018. Chalk it up to lack of awareness or other shortcomings, but companies leave themselves and their customers exposed to bad actors when they shun this kind of compliance.
Beyond merely leaving themselves and their customers vulnerable to data breaches and cyberattacks, this decreased regard for the best practices pertaining to collecting payment card data and other personally identifiable information leaves these companies on the hook for noncompliance fees. It might not be as exciting or interesting as a professional athlete paying his or her commission for uttering an expletive during a game, but it can still be just as expensive.
-
What Does PCI Stand For, And What Does It Mean For My Business?
“PCI compliance” might sound boring and technical, but it’s a major focal point for any business that handles online credit or debit card payments. In 2019, that’s most businesses!
The internet has completely changed the way we shop and transact — where we used to go to brick and mortar stores in order to spend cash or swipe a card in exchange for the goods we want, this entire experience can now happen from the comfort of your home.
-
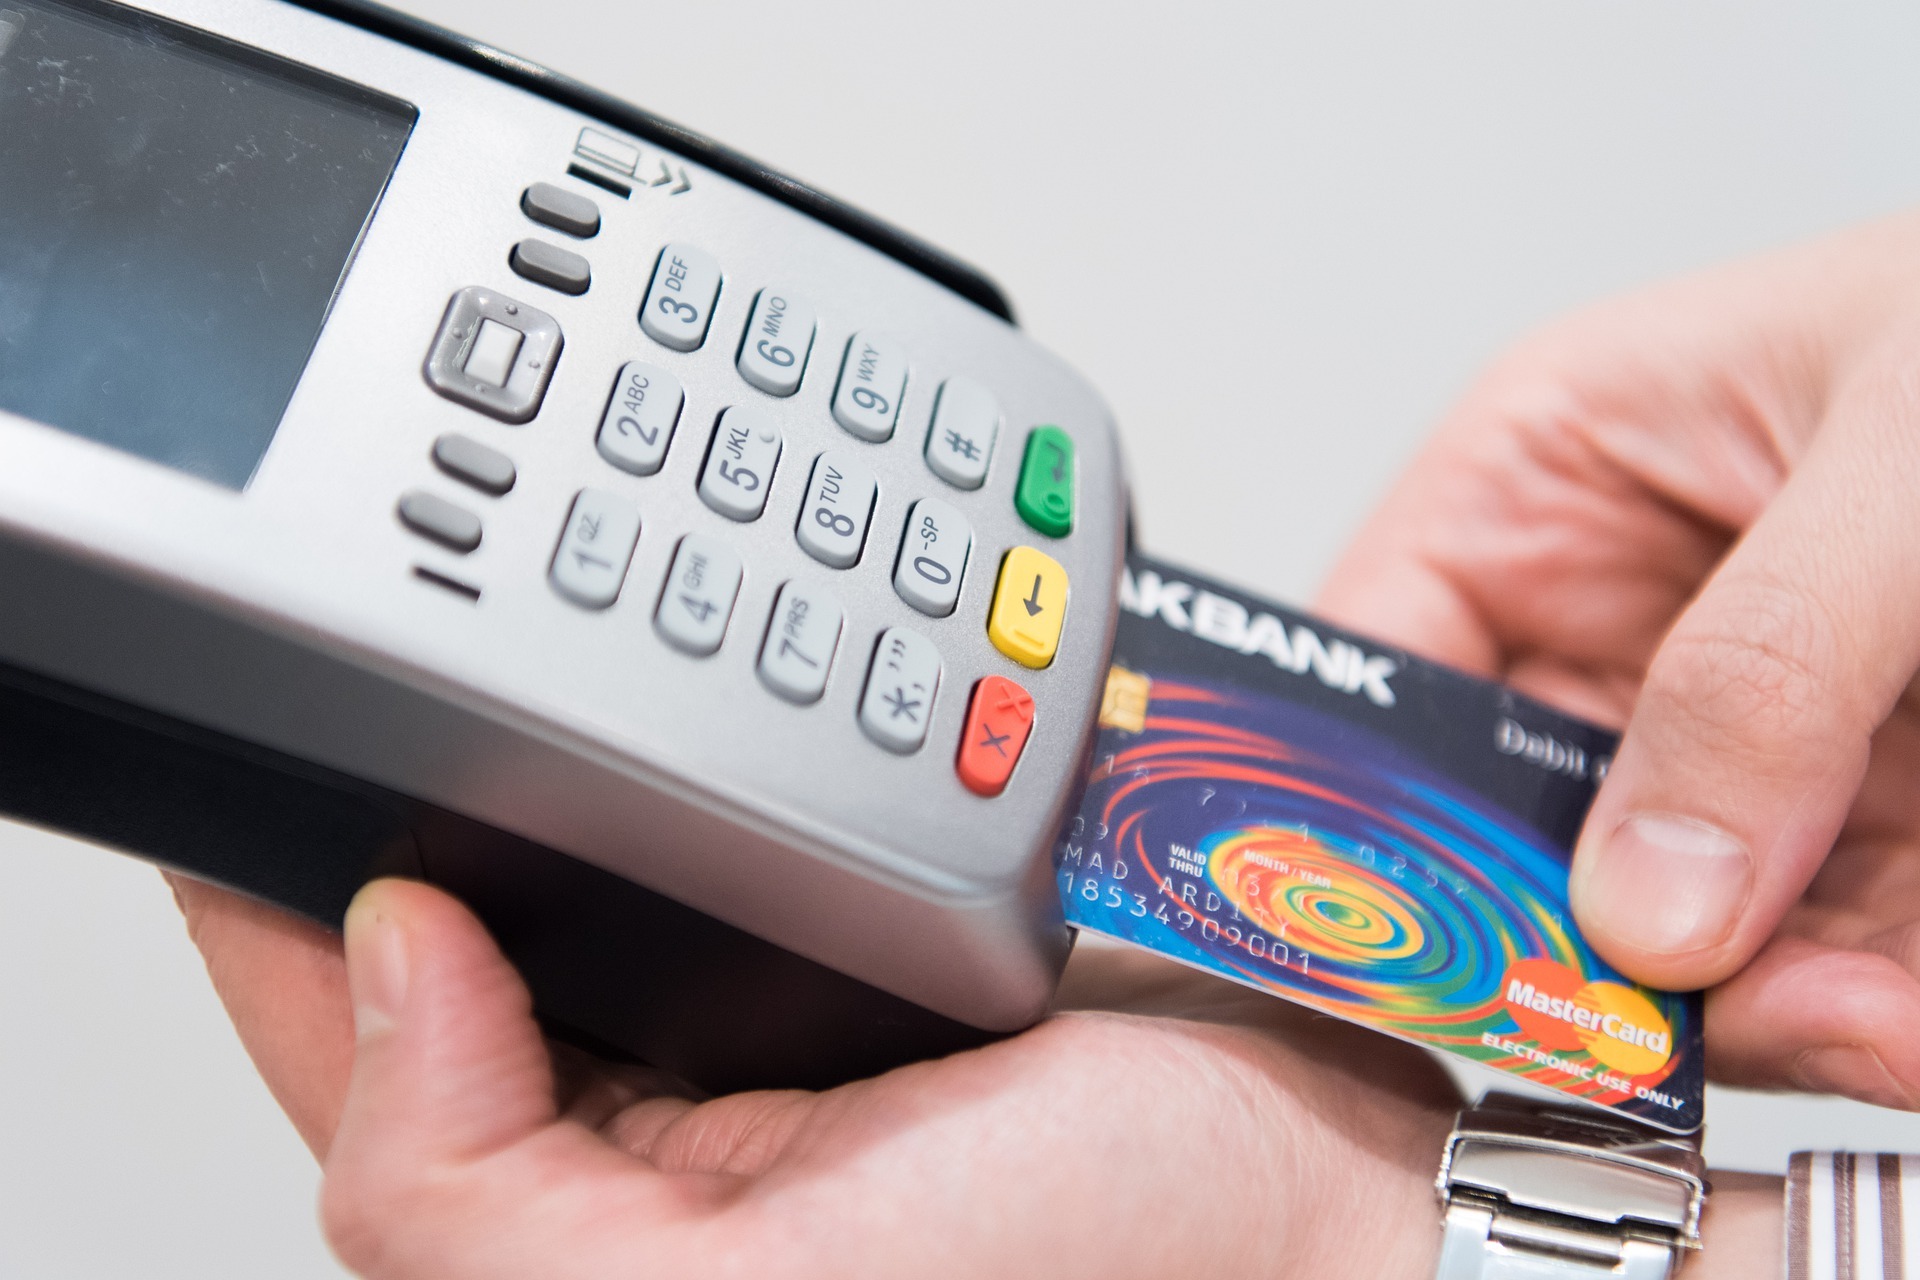
How To Become PCI Compliant — A Step by Step Guide
In times of widespread concern about cyberattacks and phishing attempts, it turns out that there’s a clear roadmap to protect your business from malicious hackers — your business only needs to pursue PCI compliance. But what is this term, and what is it all about?
Payment card industry (PCI) compliance refers to the standards that companies have to stick to in order to process payment information online. These best practices are collectively known as the Payment Card Industry Data Security Standard (PCI DSS), and they were created by the PCI Security Standards Council (PCI SSC). This set of best practices works to increase controls and protection around cardholder data while simultaneously reducing credit card fraud.
Just as you might see homes advertising the security systems they’ve installed (“protected by Brinks,” for example), PCI compliance is a similar demonstration that a company has taken steps to protect its systems and infrastructure. When you make your business PCI compliant, it represents major progress toward protecting your customers from data breaches and protecting your business against cyberattacks. It’s completely in your interest if your company processes payments online.